


VirtualCISOleadershipforcompaniesthatrefusetobethenextheadline.
We've run security where failure wasn't an option. Now we're the fractional CISO for mid-market companies: clean audits, a board that trusts the numbers, and one senior leader who owns it all.



What we do
Senior security practice. Three things, done properly.
Strategic leadership and deep technical execution under one roof. Talk to a real CISO about which of these fits your business.
Security leadership & governance
A senior CISO who has run real programs at Fortune 100 scale, setting your strategy, owning the risk program and answering to your board.
Commercial audits (SOC 2, ISO 27001, HIPAA) and federal mandates (CMMC) are treated as different problems, because they are.
Threat operations & response
Detection, hunting and incident command from operators who have run real investigations, with a senior responder on the line when something is actually happening.
Tabletop exercises and an incident retainer mean your plan has been tested before the day you actually need it.
Architecture & AI agent security
Zero-trust and cloud foundations that scale with you, plus guardrails for the AI agents and non-human identities your teams add faster than anyone reviews.
Delivered on Radius360, the platform we built to run our own practice: agents propose, practitioners ratify. No unverified automated claims.
Security rarely fails for lack of a plan. It fails in the gap between the plan and the people who have to run it.
A strategy no one executes leaves the risk exactly where it was. Tools with no owner get pointed at the wrong problems. In practice, that gap looks like this:
A prospect sends a SOC 2 questionnaire, and nobody actually owns the answer.
A framework sits on the roadmap for a year with no one running the program behind it.
The tool stack keeps growing while the risk it was bought to close never does.
Why BlueRadius
Built by the people who have to run it.
We have run security where getting it wrong was not an option: at Fortune 100 scale, and inside growth-stage teams that inherited the whole problem overnight.
The same pattern showed up every time. No shortage of advice, no shortage of tools, and no one senior actually closing the loop. BlueRadius is the practice those teams needed. Radius360 is the platform we built to run it.
Two ways to work with us
Strategy, and the platform to run it, from one team.
Services
Fractional security leadership
Virtual CISO leadership, managed security, and audit-ready compliance, run by senior practitioners who have done it at Fortune 100 scale.
Explore servicesPlatform
Radius360
The security program platform we build on: it turns your signals into decisions with the evidence attached, across 30 frameworks.
Explore Radius360Not sure where you stand?
Book a free consultationTechnology partners
We deploy and manage industry-leading security platforms across every engagement.


Field reports
Two engagements, in the client's own words. Both ended with a program the team runs without us.
“Getting SOC 2 certified is a marathon, most companies take over a year. BlueRadius got us there in eight months. We passed our first audit with zero findings. That certification opened doors to enterprise clients we couldn't touch before.”
A security program they actually understand.
Director of Engineering, SaaS Platform
“What sets BlueRadius apart is they don't just advise, they execute. They embedded with our team, trained our engineers, and left us with a security program we actually understand and can maintain.”
The difference
Why BlueRadius.
Most security firms sell tools or paperwork. We sell judgment, earned over a career of running programs that had to actually hold up.
Senior practitioner, not a vendor
We execute, not just advise
Security as business advantage
Outcomes, not deliverables
Leadership
Built by people who've done it.
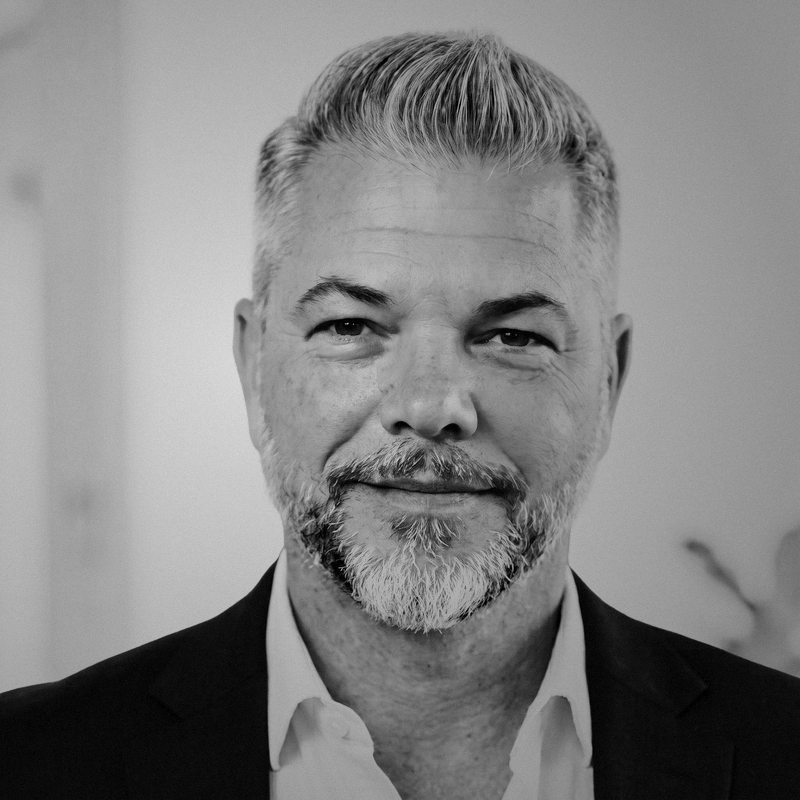
Jeff Sowell
Founder and Managing Principal
CISSP · M.S. · Veteran · Former CISO
"I built BlueRadius because I was tired of watching companies treat security like a checkbox. Real protection takes leadership, not playbooks."
Former Head of Product Security at Ericsson. Built security programs for Microsoft, L'Oréal, and the U.S. Department of Health and Human Services. More than thirty years of running real programs and briefing real boards.
Connect on LinkedIn
Matthew Hedger
Advisory Board Member
Former CIA · NSA · USN Veteran
"Real-world security isn't about playbooks. It's about judgment, knowing when the rules apply and when they don't."
Partner and Chief Consultant at Busoni Global. Former CIA Operations Officer and NSA cryptologist. Led intelligence operations through deep-cover missions and high-stakes investigations.
Connect on LinkedIn
Aaron Long
VP Security Operations / Field CISO
CISSP · M.S. · 15+ Years
Builds and runs the operational engine. SOCs, MDR programs, and security teams that scale across hundreds of client environments.
Former VP of Operations at OneAxiom and SOC Manager at ZeroFox. Senior consultant for Continent8 Technologies in gaming and hospitality. Fifteen years building and scaling SOCs and MDR programs.
Connect on LinkedInGet in touch
Ready when you are.
No pitch deck. No runaround. A direct conversation with a senior practitioner about what you actually need.
Or send a message