What Is a Virtual CISO (vCISO)? Role, Responsibilities and When You Need One
A virtual CISO (vCISO) is an experienced CISO who leads a company's security program part-time. Here is what a vCISO does, how the role differs from a full-time CISO, an MSSP or a consultant, and the signs a company needs one.
A virtual CISO (vCISO) is an experienced Chief Information Security Officer who leads a company's security program part-time, usually under a monthly retainer. They own the same decisions a full-time CISO would: what to fix first, which framework to pursue, how much risk to accept and what to tell the board. They just are not on the payroll full-time. You will also see the role called a fractional CISO, a part-time CISO or an outsourced CISO. They all mean the same thing.
The model exists because of a simple budget problem, and the numbers make it plain.
Why most mid-market companies cannot afford a full-time CISO
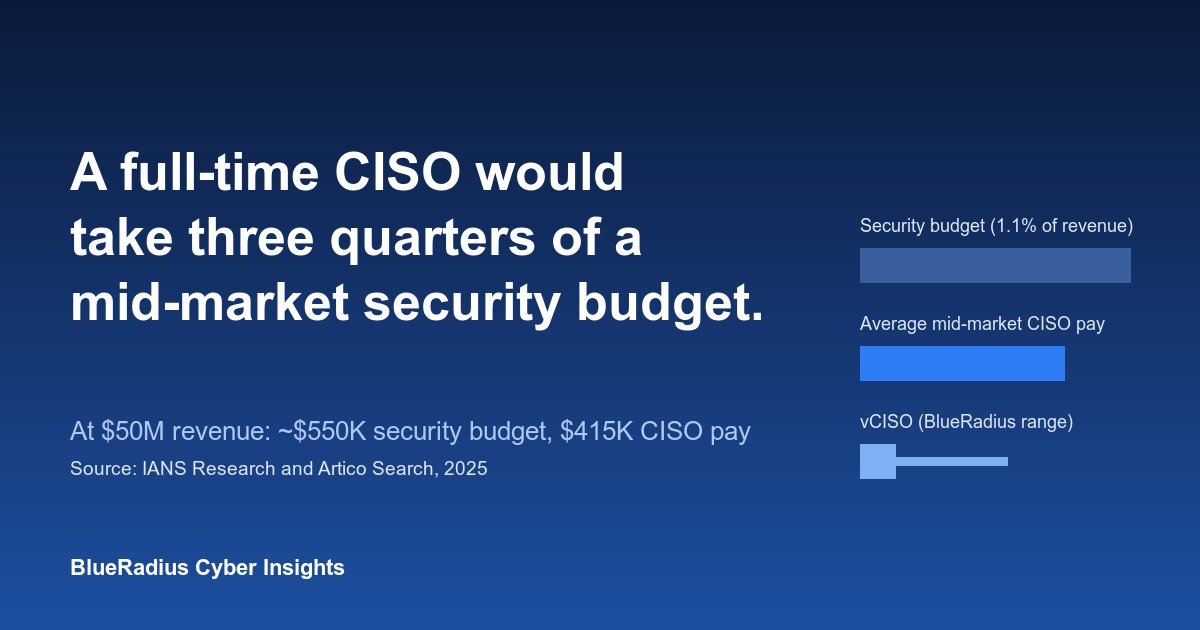
IANS Research and Artico Search surveyed 363 CISOs at organizations with up to $1 billion in revenue for their 2025 small and mid-market compensation and budget report. Two findings matter here:
- Average total compensation for those CISOs was $415,000.
- Their security budgets averaged 1.1% of company revenue, or about $11,000 for every $1 million.
Put those together for a company with $50 million in revenue. At 1.1%, the entire security budget is about $550,000 a year. A CISO paid the mid-market average would take roughly three quarters of it, before a single tool, audit or analyst. At $20 million in revenue, the budget is about $220,000, which does not cover the salary at all.
That gap is what a vCISO closes. BlueRadius vCISO engagements run $6,000 to $25,000 a month, or about $72,000 to $300,000 a year, depending on scope. That leaves most of the budget for the work itself.
Larger companies face the same squeeze in a different form. IANS and Artico's 2025 compensation report, based on 566 CISOs in the U.S. and Canada, found CISO pay rose an average of 6.7% in 2025 while security budgets grew only 4%, the slowest growth in five years.
What does a virtual CISO actually do?
A vCISO owns the security program, not a list of tickets. In practice that means:
- Setting priorities. Deciding what gets fixed this quarter and what waits, based on the risks that matter to the business rather than the loudest alert.
- Running the risk register. Keeping a current, owned list of security risks, with a decision recorded against each one: fix, accept, transfer or avoid.
- Leading compliance. Choosing and running SOC 2, HIPAA, ISO 27001, CMMC or PCI DSS programs, and preparing for the audit.
- Reporting to leadership and the board. Turning technical findings into decisions executives can make and defend.
- Writing and maintaining policy. Policies that describe what the company actually does, not templates that sit in a folder.
- Owning vendor and third-party risk. Reviewing the suppliers that hold your data or touch your systems.
- Leading incident response. Owning the plan, running tabletop exercises and making the calls when something happens.
What a vCISO is not: a help desk, or a security operations center watching alerts overnight. That is managed security, a different service with a different price. Many companies need both, and a good vCISO will tell you which monitoring you actually need.
Why demand for vCISOs is rising
Three pressures are pushing more companies toward named security leadership.
Customers and auditors ask for it. Enterprise buyers now send security questionnaires before they sign, and SOC 2 and ISO 27001 auditors expect clear, assigned responsibility for the security program.
Regulators ask about expertise. Since the SEC adopted its cybersecurity disclosure rules in July 2023, public companies must describe in their annual 10-K how the board oversees cybersecurity risk and "management's role and expertise in assessing and managing material risks from cybersecurity threats." Private companies that sell to public ones, or plan to go public, feel the same expectation.
The service is now easy to buy. Cynomi's State of the Virtual CISO 2025 survey of 200 senior leaders at North American MSPs and MSSPs found that 79% see high demand for vCISO services among small and mid-size businesses. As reported by Help Net Security, 67% of those providers now offer vCISO services, up from 21% in 2024. Cynomi sells software to vCISO providers, so read those figures as a provider-side view of demand.
How is a vCISO different from a full-time CISO, an MSSP or a consultant?
- Full-time CISO: the same accountability, there every day, at the cost covered above. The right choice once security decisions fill a full working week, usually at larger or heavily regulated companies.
- vCISO: the same accountability, part-time. The program has to be organized enough that work keeps moving between sessions.
- MSSP (managed security service provider): runs monitoring and response, often 24/7. It operates tools; it does not decide your priorities or report your risk to the board.
- Consultant: delivers a defined project, such as an assessment or a policy set, and then leaves. A vCISO stays and owns the outcome.
For the cost side of this comparison in more detail, see our guide to vCISO cost and the comparison of fractional and full-time CISOs.
When does a company need a virtual CISO?
The usual triggers are specific and easy to spot:
- A customer or prospect asks for SOC 2, ISO 27001 or a completed security questionnaire, and nobody owns the answer.
- The board, investors or a lender start asking about cyber risk.
- A regulation applies to you for the first time: HIPAA, CMMC, PCI DSS, or state privacy law.
- Your cyber insurance renewal asks questions you cannot answer with confidence.
- You had an incident, or a near miss, and it was not clear who was in charge.
- You own a lot of security tools but cannot say what risk each one reduces.
- You are buying or selling a company and need security due diligence.
If two or more of these apply, a vCISO is usually cheaper than continuing without one. Our list of questions every board should ask is a useful self-check.
How do you choose a vCISO?
Ask these before you sign:
- Who exactly will be our CISO, and how many other clients do they carry?
- What is included each month, and what is billed separately?
- Have you taken companies like ours through the framework we need, and can we speak to one?
- How will you report progress to our leadership and board?
- What happens to our policies, risk register and evidence if we part ways?
Be wary of anyone who leads with a tool before understanding your business, who cannot name the person doing the work, or who promises a certification date before seeing your environment. We cover this in more depth in questions to ask before hiring a vCISO, and the first months of an engagement in our 90-day implementation guide.
Frequently asked questions
How much does a virtual CISO cost?
BlueRadius engagements run $6,000 to $25,000 a month depending on scope: the number of frameworks, how much board reporting is involved, regulated data and incident response coverage. Other providers price hourly or per project, so compare what is included, not just the headline number.
Is a fractional CISO the same as a virtual CISO?
Yes. Fractional CISO, virtual CISO, vCISO, part-time CISO and outsourced CISO all describe the same role: an experienced security leader who owns your program part-time.
Does a virtual CISO work remotely?
Mostly, with on-site time for board meetings, workshops, audits and incidents. Most of the work, reviewing risk, guiding the team and preparing reports, does not need someone in the building.
Can a virtual CISO attend board meetings?
Yes, and they should. Presenting security risk to the board in business terms is one of the main reasons companies hire one.
When should a company move from a vCISO to a full-time CISO?
When security decisions genuinely fill a full working week: usually at larger scale, in heavily regulated industries, or when the security team grows big enough to need a full-time leader every day. A good vCISO will tell you when that point arrives and help you hire for it.
Sources
- IANS Research and Artico Search, "IANS and Artico Search Release Compensation and Budget Report for CISOs in the Small and Middle Market", June 17, 2025. Survey of 862 security executives, including 363 CISOs at organizations with up to $1 billion in annual revenue, April to December 2024.
- IANS Research and Artico Search, "New Report from IANS and Artico Search Shows 6.7% Rise in CISO Compensation in 2025", November 13, 2025. Self-reported data from 566 CISOs in the U.S. and Canada.
- U.S. Securities and Exchange Commission, "SEC Adopts Rules on Cybersecurity Risk Management, Strategy, Governance, and Incident Disclosure by Public Companies", press release 2023-139, July 26, 2023.
- Cynomi, "The State of the Virtual CISO 2025". Survey of 200 senior security leaders at North American MSPs and MSSPs with 50 or more employees, fielded by Global Surveyz in May 2025.
- Help Net Security, "AI is changing the vCISO game", July 31, 2025.
Related from the BlueRadius Library
Sourced posts on adjacent topics, ranked by tag overlap.
vCISO
Virtual CISO vs. Building an Internal Security Team in Dallas-Fort Worth: A Cost and Capability Analysis
Virtual CISO vs building an internal security team in Dallas-Fort Worth: cost comparison, capability analysis, and when each model makes sense.
ReadvCISO
Why GRC Platforms Fail Without vCISO Guidance: The Strategic Gap in Compliance Automation
GRC tools automate workflows but cannot make decisions. See why platforms underdeliver without vCISO guidance, and how expert oversight closes the gap.
ReadvCISO
Virtual CISO for Manufacturing: Complete OT/IT Security Leadership Guide
A vCISO brings OT and IT security leadership to manufacturers: ICS and SCADA protection, regulatory compliance, and executive strategy without a full-time hire.
ReadvCISO
How to Choose a Virtual CISO Provider: Complete Buyer's Guide for 2025
A 12-point framework for evaluating virtual CISO candidates: credentials, industry depth, engagement models, references, scope, and red flags to avoid.
ReadvCISO
Virtual CISO for FedRAMP Compliance: Federal Cloud Security Leadership Without Full-Time Cost
Reach FedRAMP authorization with experienced federal security leadership from a vCISO, at 50 to 70% less than a full-time hire over 12 to 18 months.
ReadvCISO
When to Transition from vCISO to Full-Time CISO: The Strategic Growth Decision Framework
The signals it's time to move from a vCISO to a full-time CISO: headcount, regulatory load, board demands, and budget. A practical decision framework.
ReadRelated services